Updated October 27, 2026.
Your SaaS website looks ready. Pricing is approved, signup works on the developer’s laptop, and the payment sandbox returns success. What evidence would justify opening it to customers?
Before launch, ask an independent QA provider for a defined scope, a journey-by-browser test matrix, reproducible defects, fix-verification results and a release summary showing unresolved and untested risks. A checklist is useful only when it connects a customer action to an expected outcome and recorded evidence.
This buyer checklist helps you evaluate website testing services for a SaaS launch. All scenarios below are illustrative planning examples, not findings from a Testers HUB client project.
1. Ask for a scope that follows the customer beyond the website
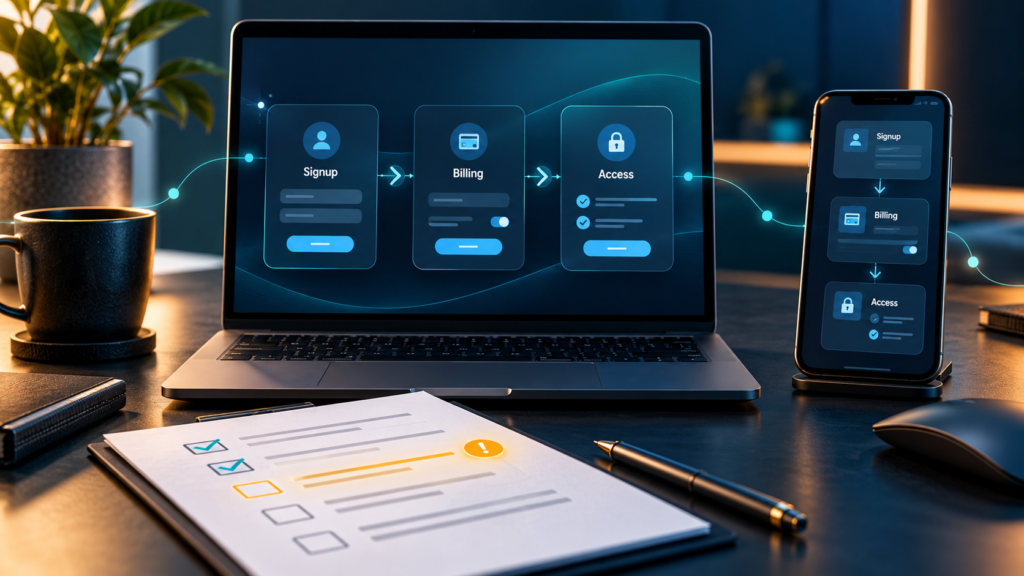
A public website, signup service and application dashboard can belong to different systems. Agree where testing starts and ends. For self-service SaaS, follow pricing through account creation, verification, payment and first access. For sales-led SaaS, follow the demo request through CRM creation and sales notification.
Ask the provider to record:
- The candidate build, environment and launch decision date.
- Priority journeys, account states, roles and expected outcomes.
- Connected services, available sandboxes and inaccessible destinations.
- Included checks, exclusions and the person who resolves unclear requirements.
Use web app testing services when coverage extends into permissions, workspace boundaries or application workflows. General website QA should not silently imply penetration testing, load testing or formal accessibility certification.
2. Request a matrix of checks, expected results and evidence
“Signup tested” is too vague. It can mean one successful registration in an existing session. Ask for starting conditions and outcomes that another tester could repeat.
The following matrix is a starting scope, not an executed report. Every row begins as Not run; replace assumptions with your product’s approved rules.
| Journey | Check | Expected result | Evidence |
|---|---|---|---|
| Pricing to signup | Choose annual billing, register and verify in a new tab | The agreed plan and billing period survive the journey | Selection, account state and checkout summary |
| Account verification | Open an expired link, then request another | Clear recovery without unintended duplicate accounts | Messages, timestamps and resulting account state |
| Payment to access | Exercise success, failure and delayed confirmation in sandbox | Payment state and permitted access follow the agreed rules | Test transaction reference and entitlement state |
| Demo request | Submit approved synthetic details once | The intended CRM record and sales notification are produced | Submission reference, record ID and inbox receipt |
| Session recovery | Let a session expire before saving | Reauthentication and input handling follow requirements | Before/after state and recovery recording |
| Workspace access | Use an authorized test account to open another test workspace’s URL | Access respects the documented boundary | Role, test workspace and observed response |
Traceable record and inbox checks require approved access or evidence from an authorized client contact. Otherwise, mark that destination unverified. Our CRM lead-delivery walkthrough explains the handoffs.
3. Ask what happens when the successful path breaks
Negative testing should explain recovery, not merely show an error message. Prioritize conditions that leave users unsure whether an action completed:
- Submit twice while the first request is still loading.
- Refresh or navigate back during registration or checkout.
- Interrupt connectivity after submission but before confirmation.
- Retry after the account exists but notification delivery failed.
- Open a saved link after logout or a permission change.
Ask which system determines the final outcome and how the UI reconciles it. A retry should follow the product’s duplicate-handling rules. A loading indicator should eventually resolve into a meaningful result or recovery path.
For authorization checks, agree permitted test accounts and boundaries. OWASP’s authorization-testing guidance describes checking access against roles and privileges. Focused functional permission checks do not replace a specialist security assessment.
For checkout, distinguish a declined payment from an uncertain result after a connection loss. Check the authorized transaction state before suggesting another payment. Close the browser before returning from checkout, then sign in through a fresh session and compare the payment record, chosen plan and available access. Where asynchronous payments are supported, test pending, success and failure against the agreed access policy.
For signup, compare annual and monthly selections after refresh, back navigation and verification in another browser. Test existing accounts and older verification links after resending. Record whether the intended selection survives or the user is clearly asked to choose again.
4. Require browser coverage by journey, not a row of logos
Ask which critical workflows run on each browser, operating system and device. Separate real hardware from emulation. Choose coverage from available audience evidence or explicit launch assumptions, then record versions at execution.
For example, a proposed matrix might include desktop Chrome and Safari plus real iPhone and Android checks. This is a planning example, not a commitment to particular devices or complete coverage on every combination.
Include mobile keyboard behavior, autofill, orientation, zoom and sticky elements that can obscure controls. Run keyboard-only form completion and check whether errors identify the affected field and explain recovery. W3C’s form-notification guidance supports clear feedback for both failed and successful submissions.
5. Ask to see a reproducible defect and its retest record
Illustrative defect: a new user selects annual billing, verifies their email in another tab and reaches a monthly checkout summary. This example demonstrates reporting expectations; it does not claim a real project outcome.
The report should include the build, environment, account state, browser/device, exact steps, expected billing period, observed result, frequency and sanitized evidence. A useful attachment shows the original selection and resulting summary. Severity depends on impact and affected users, not the length of the report.
Fix verification repeats this failure on the corrected build. Regression checks adjacent paths, such as monthly signup, existing-account purchase and returning from verification. Keep developer-reported fixes separate from QA-confirmed results.
6. Agree the evidence needed for a release decision
A completed test cycle is not automatically a release approval. Request a summary showing tested build, coverage, passed and failed checks, blocked work, unresolved defects and exclusions.
Use a simple decision framework:
- Hold: an agreed release blocker remains, or a critical journey lacks enough evidence to assess.
- Review: a limitation has a documented impact, workaround and accountable decision owner.
- Consider release: agreed criteria are met and the product owner accepts the remaining risks.
Define these criteria before execution. Also agree any production smoke check, permitted test data and cleanup. A staging result cannot establish behavior for an untested production configuration.
7. Compare outsourced QA by scope and follow-up effort
When evaluating outsourced website QA or SaaS testing services, compare the same journeys, roles, environments and deliverables. Clarify who prepares test data, answers developer questions and maintains the checklist after launch.
Ask whether retesting is included, separately charged or prioritized within reserved hours. Testers HUB’s fixed website testing packages separate initial testing from retesting and regression. Confirm current terms and the actual workflow fit before selecting a plan.
For US teams, agree collaboration hours and triage ownership rather than assuming a timezone arrangement. If you need to hire website testers repeatedly, request a maintained regression set and an explicit handover process.
8. Questions buyers should ask before commissioning launch QA
When should independent testing start?
Agree scope while the release is being prepared. Start execution when the target build, required integrations and test accounts are usable, leaving time for fixes and verification.
Is developer testing enough?
Developer tests remain essential. Independent QA adds a separate examination of customer journeys, assumptions and environments. Ask how the two sources of evidence will complement each other.
Does every page need the same testing depth?
No. Prioritize account access, purchases, lead delivery and other high-impact journeys. Sample repeated layouts where justified and document what the sample does not cover.
What if the CRM or payment sandbox is unavailable?
Record the affected checks as blocked or unverified. Simulated responses can support limited testing, but should not be reported as verified integration delivery.
Does a passing checklist guarantee a defect-free launch?
No. Results apply to tested conditions and builds. The release decision still needs unresolved risks, exclusions and a plan for handling problems after launch.